
Deepfakes and Financial Fraud: The New Frontier of AI Scams
Deepfakes are no longer just viral videos. From voice cloning scams to synthetic video calls, AI impersonation is becoming a major tool in financial fraud. Explore the legal, psychological, and ethical implications of deepfake abuse.
On this page
When people first heard about deepfakes, the conversation mostly revolved around novelty. Videos of celebrities saying things they never said circulated online, and the technology looked impressive—sometimes even amusing.
But the tone around deepfakes has shifted.
In recent years, synthetic media has moved out of the realm of internet curiosity and into something far more serious: financial scams and identity fraud. Instead of fooling thousands of viewers online, scammers now use AI-generated voices or manipulated videos to convince a single person that a trusted individual is asking for money.
And that small change in focus—from mass deception to personal manipulation—has made the technology far more dangerous.
It’s worth saying clearly, though: artificial intelligence itself is not the problem. AI is already improving everything from medical diagnostics to cybersecurity systems. The real issue lies in a specific misuse of the technology—using AI to impersonate real people without their consent.
Deepfakes turn trust itself into a vulnerability.
When the Voice on the Phone Isn’t Real
One of the most unsettling aspects of modern deepfake scams is how easily voices can now be replicated.
With today’s generative AI tools, a short recording taken from a podcast, interview, or social media video can be enough to recreate someone’s speech patterns. The resulting audio isn’t always perfect, but it doesn’t have to be. In a stressful moment, a voice that sounds close enough can be convincing.
Researchers cited by the World Economic Forum have noted that some voice-generation systems require surprisingly little training data to produce realistic speech.
Once scammers have that voice model, they can stage highly targeted attacks.
Several years ago, an employee at a European energy company received a phone call that appeared to come from the firm’s chief executive. The caller requested an urgent transfer to a supplier.
The employee authorized the payment.
Only later did investigators determine that the voice had been artificially generated. The company lost more than €220,000, according to reporting summarized by the American Bar Association.
No computer systems were hacked. Instead, the attacker exploited something much simpler: human trust.
The Emotional Side of Deepfake Scams
Corporate fraud cases tend to attract headlines, but deepfake scams increasingly target individuals as well.
One variation involves impersonating family members during staged emergencies. The scam typically begins with a distressed voice claiming to be a child or relative who has been arrested or injured. Another person then joins the call, presenting themselves as a lawyer or official who demands immediate payment.
The emotional pressure is deliberate.
In one case reported by People Magazine, a mother transferred $15,000 after receiving a phone call from what sounded exactly like her daughter.
The voice had been generated using AI.
Psychologists note that scams relying on urgency and emotional shock can bypass rational decision-making. Research discussed by the American Psychological Association suggests that fraud victims often experience intense feelings of shame or self-blame afterward—even though the deception was carefully engineered.
Deepfakes make these psychological tactics more effective because they create the illusion of familiarity.
When Deepfakes Move Into Video
Audio impersonation is only part of the story.
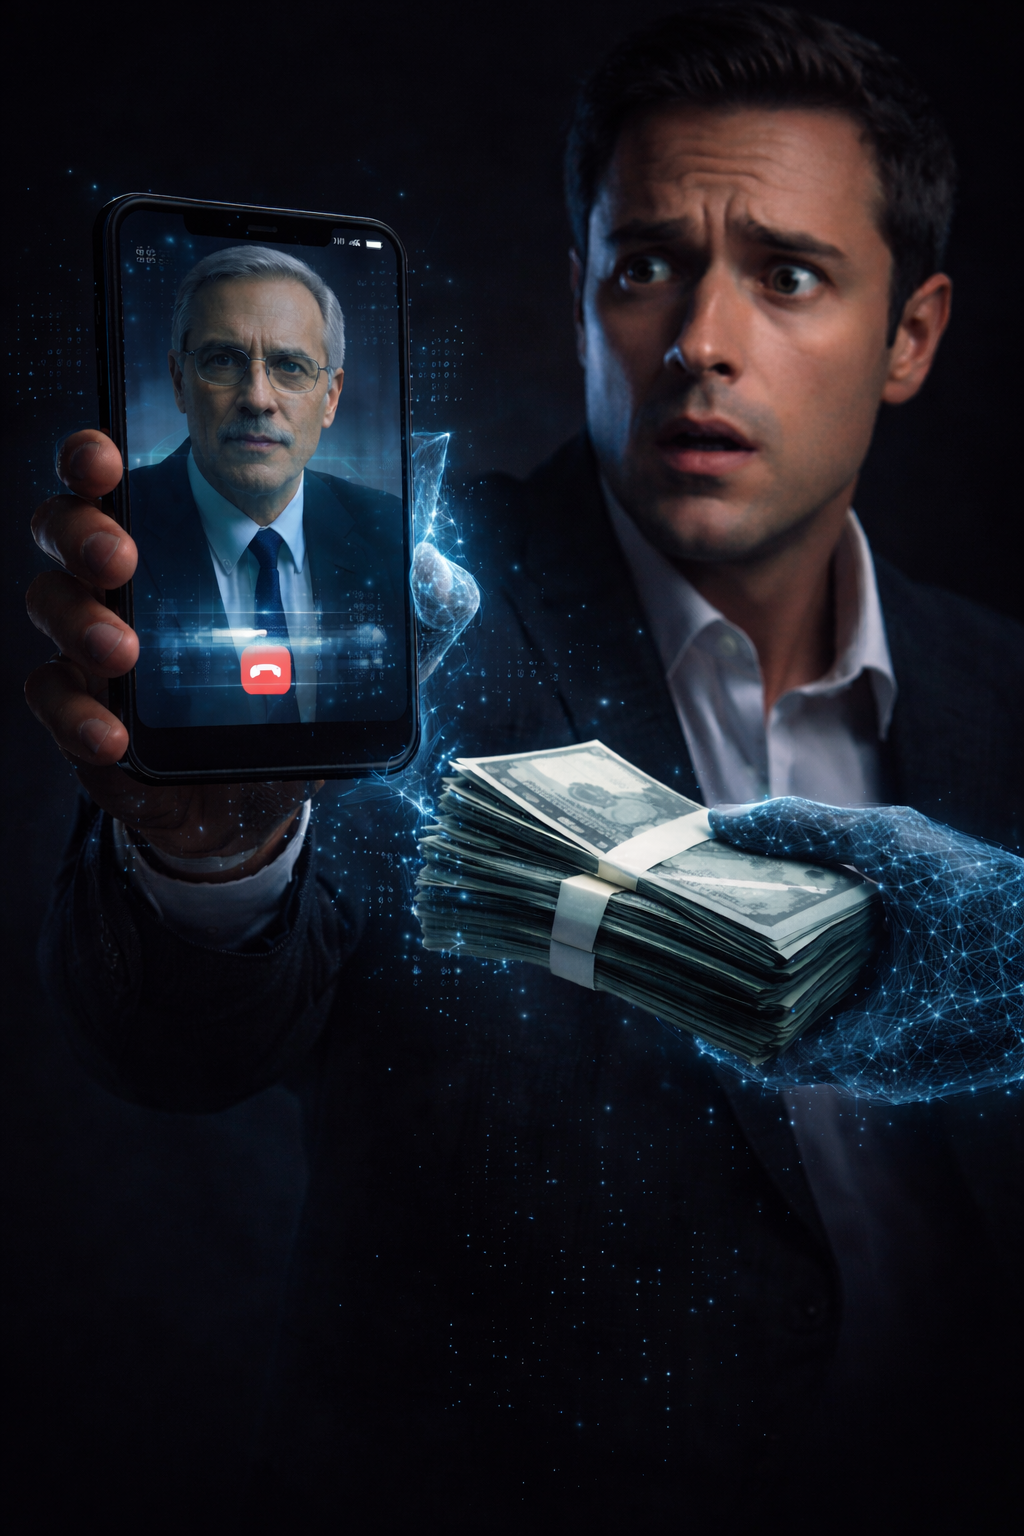
In some cases, scammers have begun using deepfake video in real-time interactions. Instead of a phone call, a victim might join what appears to be a legitimate video meeting with colleagues or executives.
But the people on screen aren’t actually there.
Investigations cited by The Guardian describe incidents in which employees transferred large sums of money after receiving instructions during video calls involving synthetic avatars.
The participants appeared real enough to avoid suspicion.
This kind of fraud highlights a troubling reality: as generative AI improves, impersonation becomes easier to scale.
The Legal System Is Still Catching Up
Deepfakes also raise difficult legal questions.
Synthetic media can violate privacy rights, enable identity theft, and damage reputations. Legislators in several countries are beginning to explore ways to regulate malicious uses of AI-generated content.
Legal experts writing for the Brookings Institution note that policymakers face a delicate balance. On one hand, laws must protect individuals from harmful impersonation and deception. On the other hand, overly broad restrictions could interfere with legitimate uses of AI technology or creative expression.
The European Union’s AI Act, for example, includes transparency requirements that may require certain AI-generated content to be clearly labeled. The goal is not to stop innovation but to reduce the risk of deception.
Still, regulation often moves more slowly than technological change.
Deepfakes and the Erosion of Trust
There is another consequence of deepfake technology that goes beyond financial fraud.
When manipulated media becomes widespread, it becomes easier to question everything—even authentic evidence.
Researchers at the Stanford Internet Observatory describe this phenomenon as the “liar’s dividend.” If people believe that videos and recordings can easily be fabricated, individuals caught in genuine wrongdoing may simply claim that the evidence is fake.
In other words, deepfakes don’t just create false content. They can weaken confidence in real information as well.
That erosion of trust may ultimately be one of the technology’s most damaging side effects.
Responsible AI Is the Real Goal
Despite these risks, it would be a mistake to view artificial intelligence itself as inherently harmful.
AI technologies are already helping doctors identify diseases earlier, enabling scientists to process massive datasets, and improving cybersecurity defenses across industries. Many financial institutions rely on machine learning systems to detect suspicious transaction patterns before fraud spreads.
Researchers at IBM Security are also exploring ways to detect synthetic media by analyzing subtle artifacts in audio or video signals.
The same technological progress that enables deepfakes can also help defend against them.
The key difference lies in intent.
When AI systems are built and used responsibly—with transparency, accountability, and consent—they can strengthen digital systems rather than undermine them.
A New Era of Verification
Deepfakes are forcing society to rethink something that once seemed obvious: how we determine what is real.
For decades, recorded audio and video carried an implicit sense of authenticity. Seeing a person speak or hearing a familiar voice was usually enough.
Today, that assumption is becoming less reliable.
But the solution is not to abandon artificial intelligence. AI remains one of the most powerful technological tools humanity has developed.
The challenge is ensuring that innovation moves forward alongside ethical safeguards.
Deepfakes represent a misuse of AI, not its future. And as detection tools improve and awareness grows, the hope is that the technology will ultimately strengthen security rather than weaken it.
Because in a world where voices and faces can be generated by algorithms, trust will depend less on appearances—and more on verification.